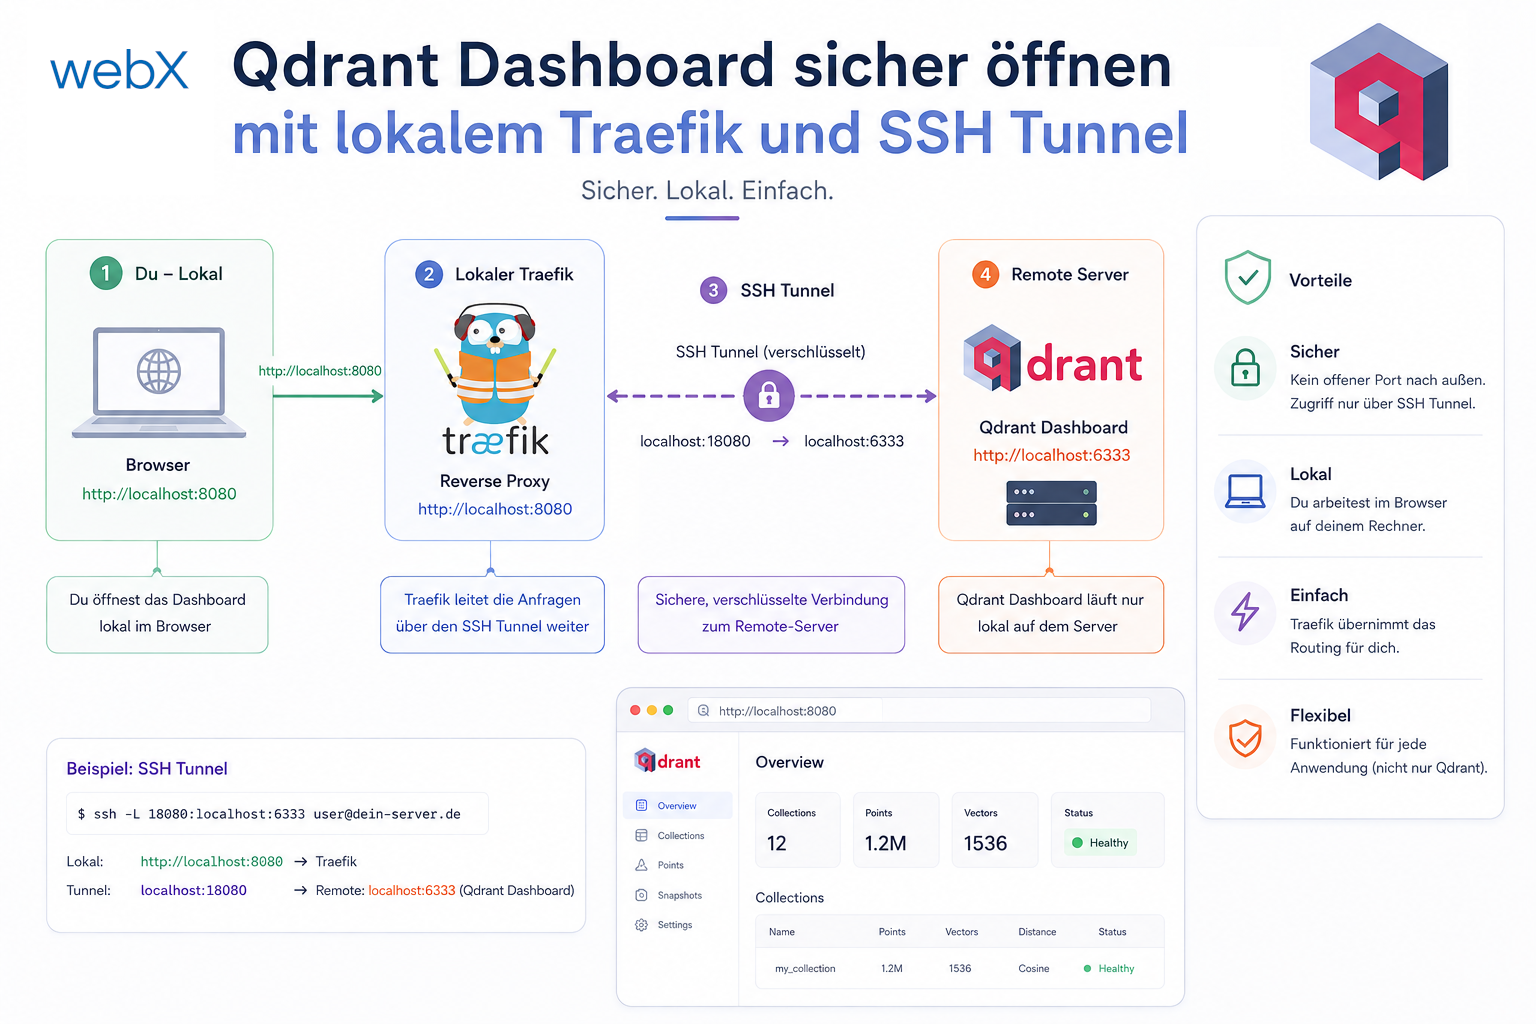
Open the Qdrant dashboard securely with local Traefik and an SSH tunnel
I wanted to inspect Qdrant data in the browser without making the database public. Locally I use Traefik; in production I open only an SSH tunnel and keep Qdrant internal.

I wanted to inspect Qdrant data in the browser without making the database public. Locally I use Traefik; in production I open only an SSH tunnel and keep Qdrant internal.
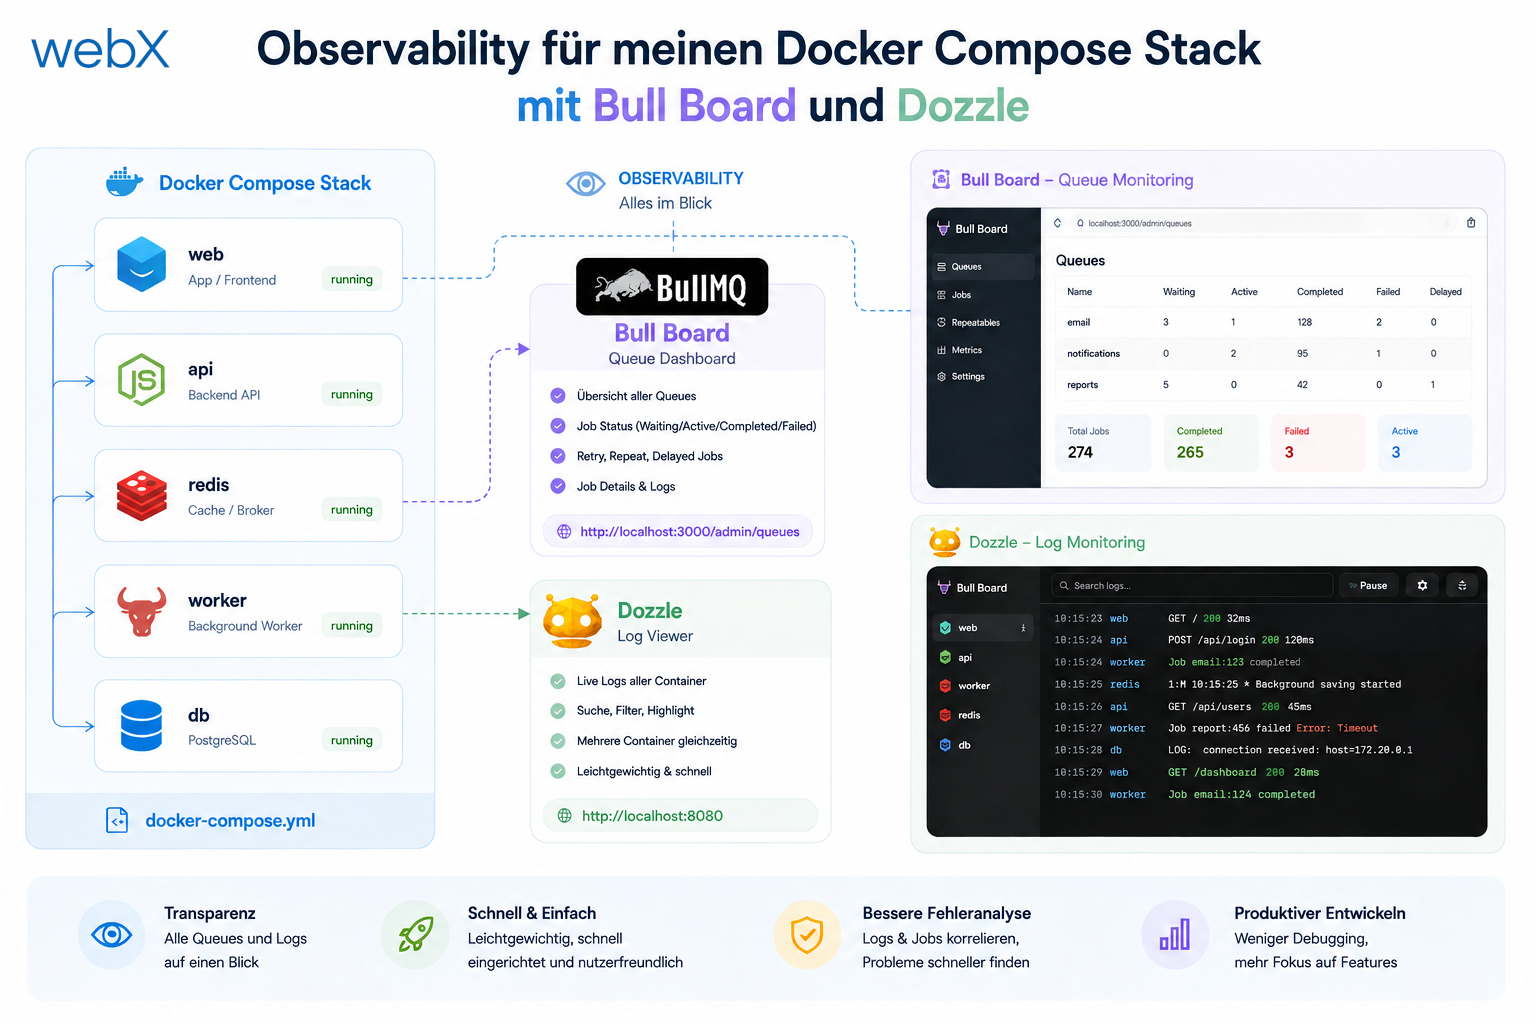
I wanted to make the path from the extension to storage visible. With Bull Board and Dozzle, I have queue status and container logs directly in the browser and can identify failures much faster.
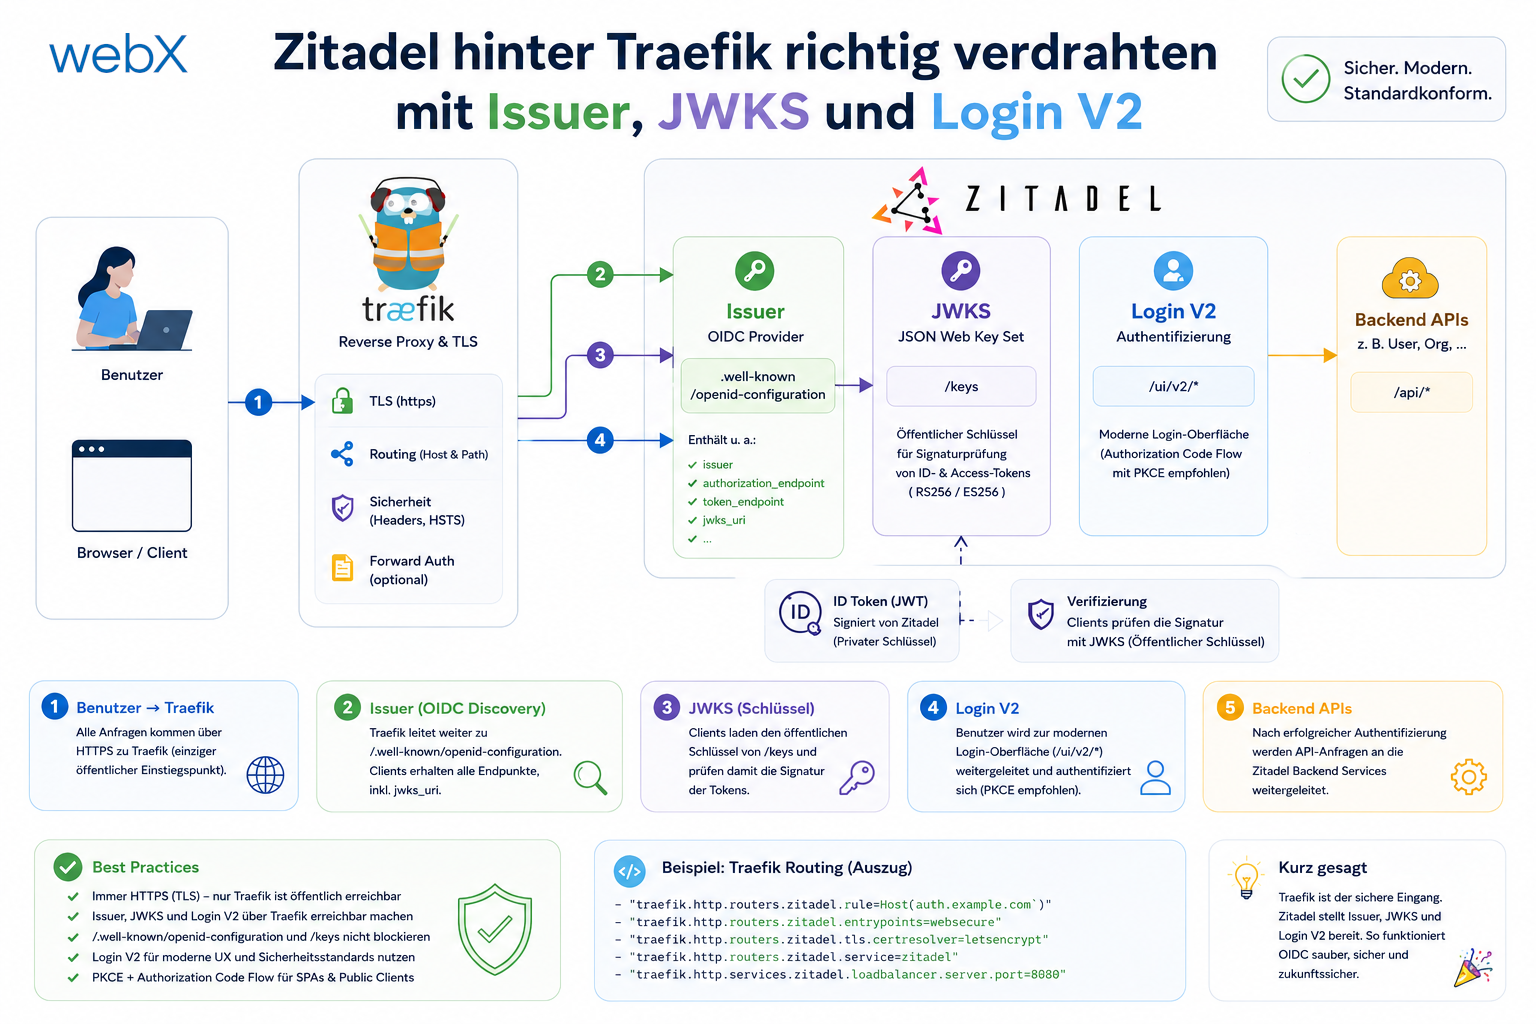
The ingest 401 error did not come from the JWT itself, but from a small architectural mismatch. Issuer, JWKS and Host headers needed the same public view of Zitadel.
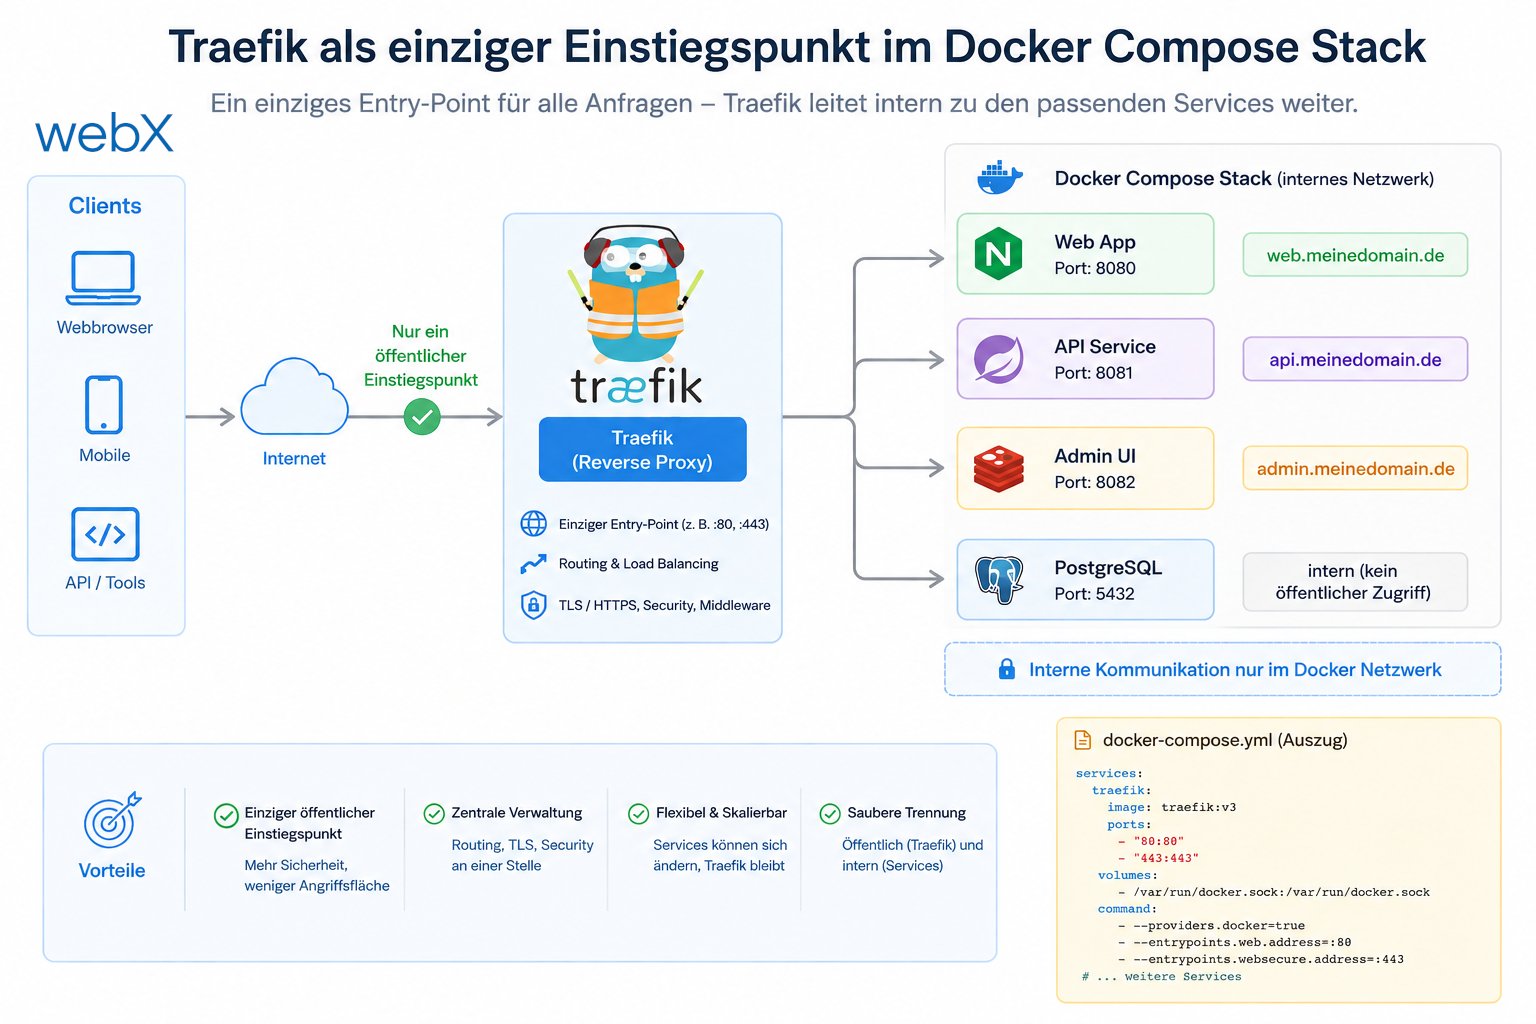
I restructured the stack so that browsers and the extension see only Traefik. Everything else runs through two Docker networks, explicit labels and no more direct host ports.
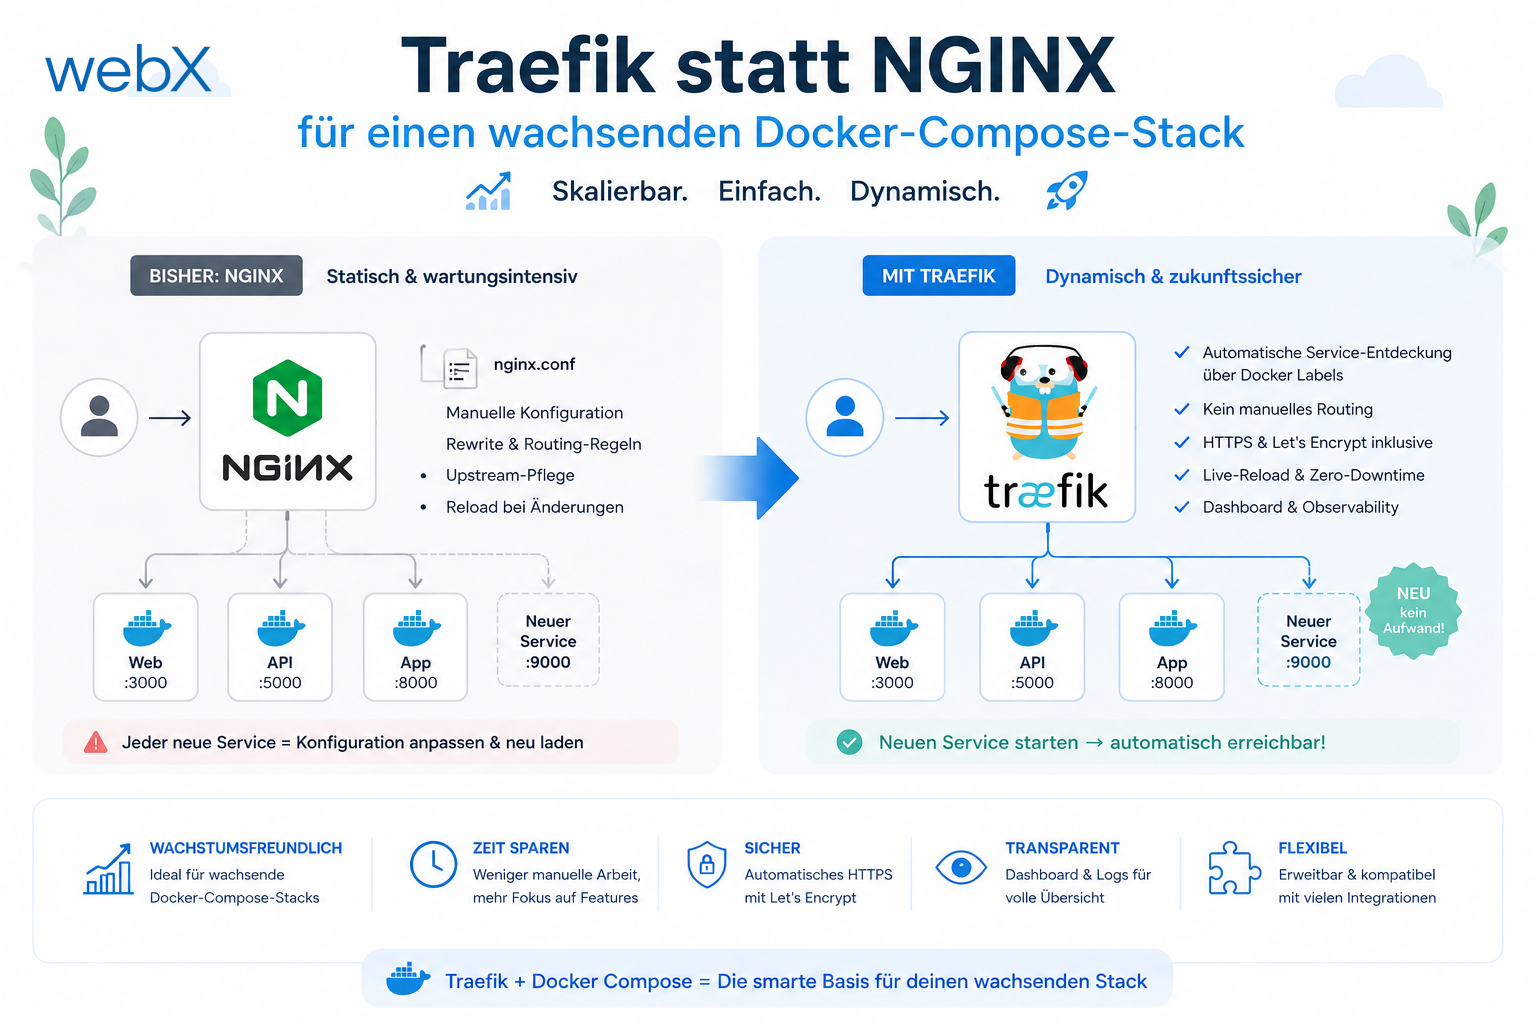
With eight services in a Docker Compose stack, nginx.conf becomes a maintenance burden. Traefik reads service configuration directly from Docker labels, terminates TLS automatically through ACME and needs no separate configuration file. Why I switched and what the configuration looks like.
Describe your workflow. Together, we will identify the right next step.
Discuss your workflow