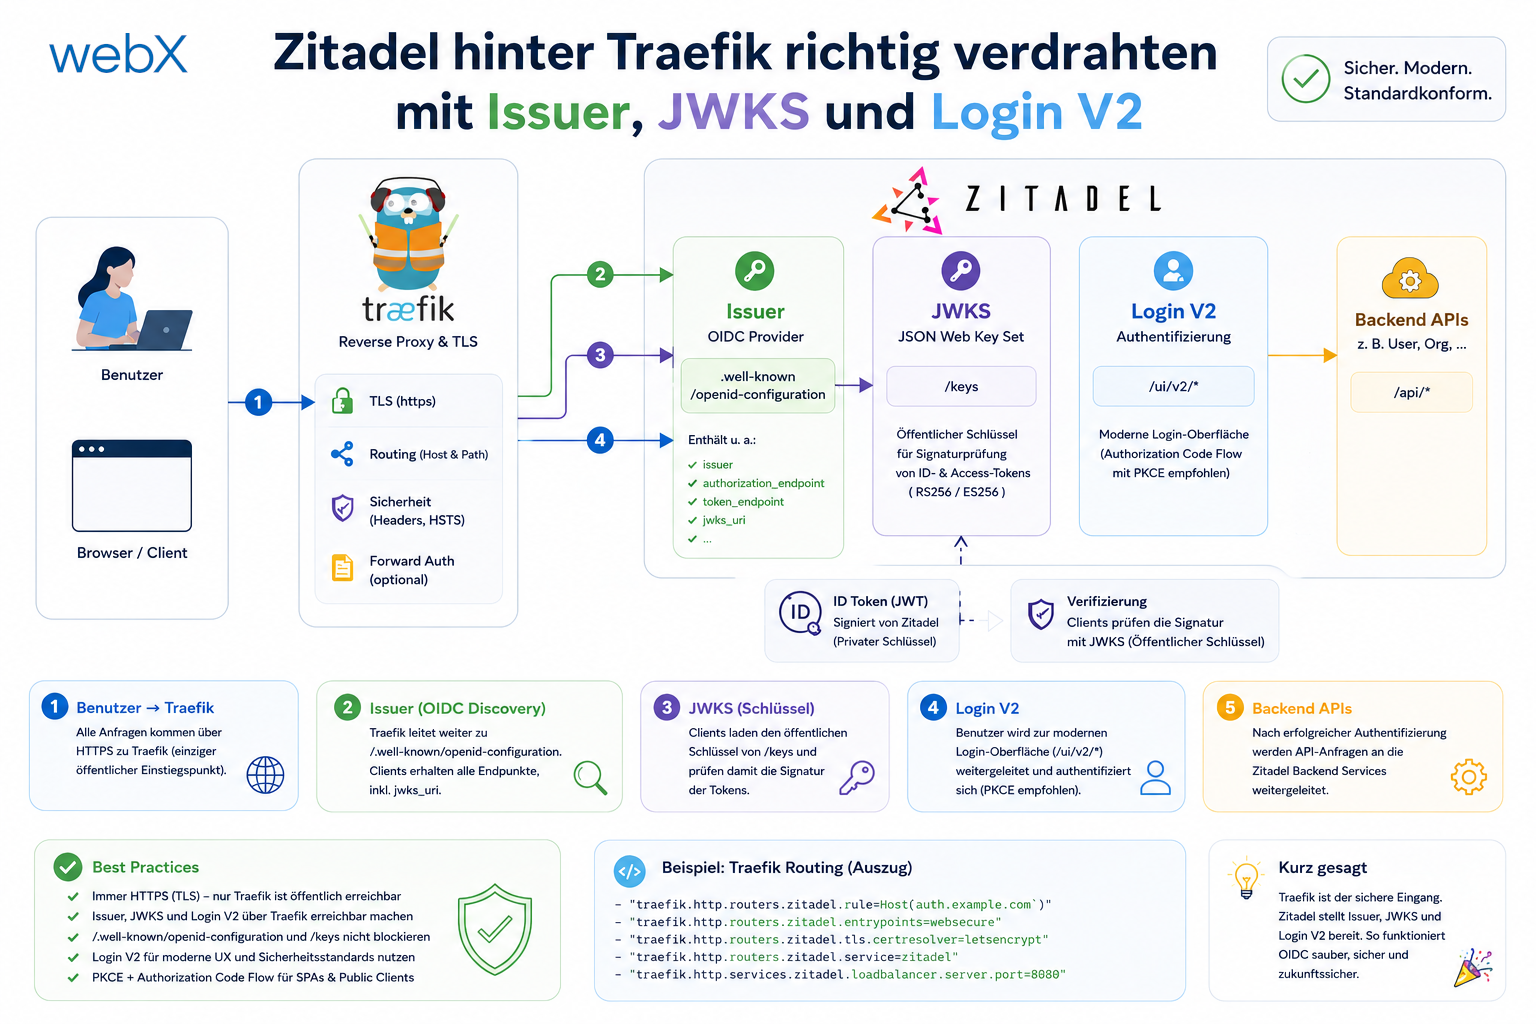
Wiring Zitadel behind Traefik with issuer, JWKS and Login V2
The ingest 401 error did not come from the JWT itself, but from a small architectural mismatch. Issuer, JWKS and Host headers needed the same public view of Zitadel.

The ingest 401 error did not come from the JWT itself, but from a small architectural mismatch. Issuer, JWKS and Host headers needed the same public view of Zitadel.
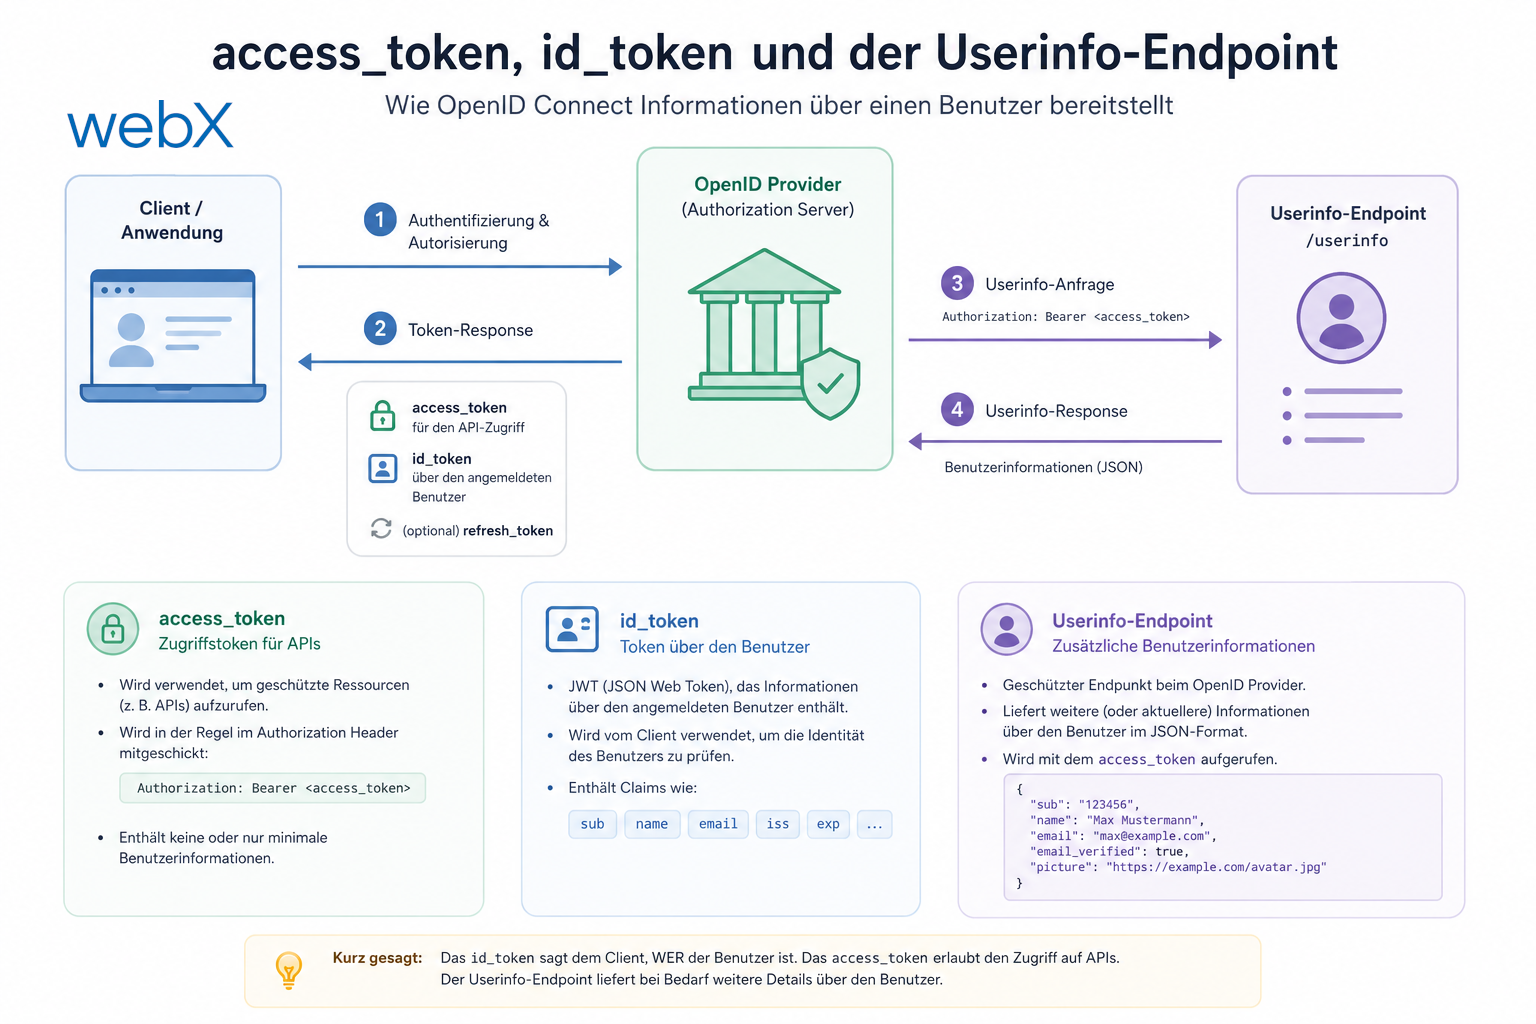
OAuth 2.0 and OIDC return two tokens at login, and almost every implementation reads the email address from the wrong one. Why access_token and id_token serve fundamentally different purposes, and why the Userinfo endpoint is the more reliable source for user profile data.
Describe your workflow. Together, we will identify the right next step.
Discuss your workflow