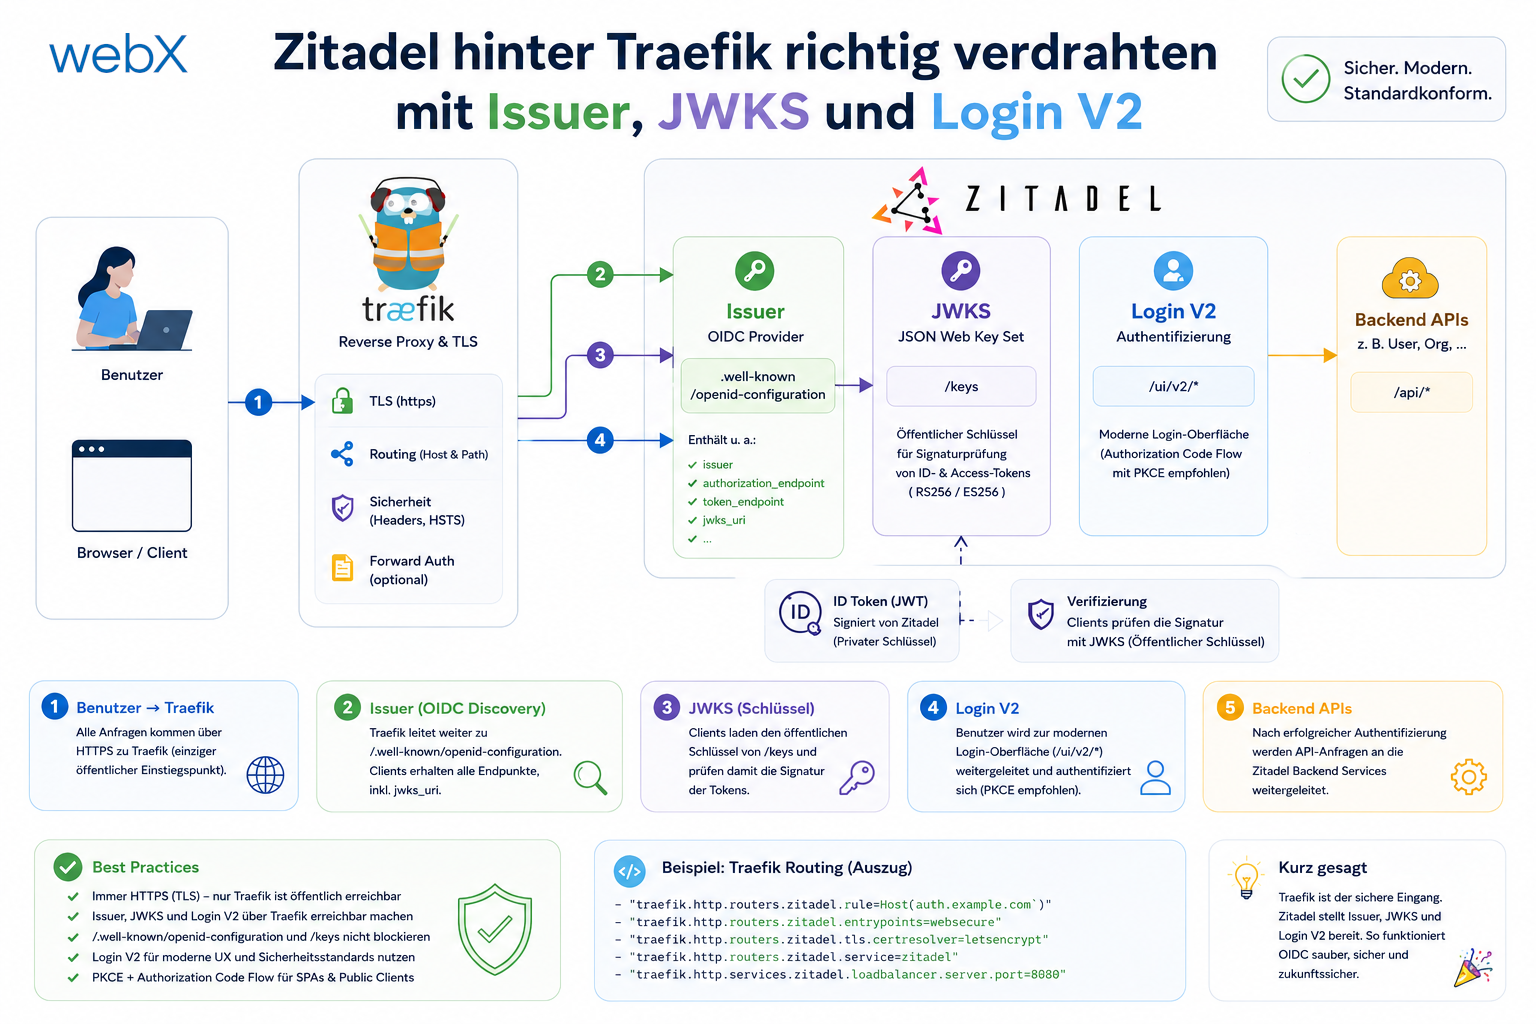
Wiring Zitadel behind Traefik with issuer, JWKS and Login V2
The ingest 401 error did not come from the JWT itself, but from a small architectural mismatch. Issuer, JWKS and Host headers needed the same public view of Zitadel.

The ingest 401 error did not come from the JWT itself, but from a small architectural mismatch. Issuer, JWKS and Host headers needed the same public view of Zitadel.
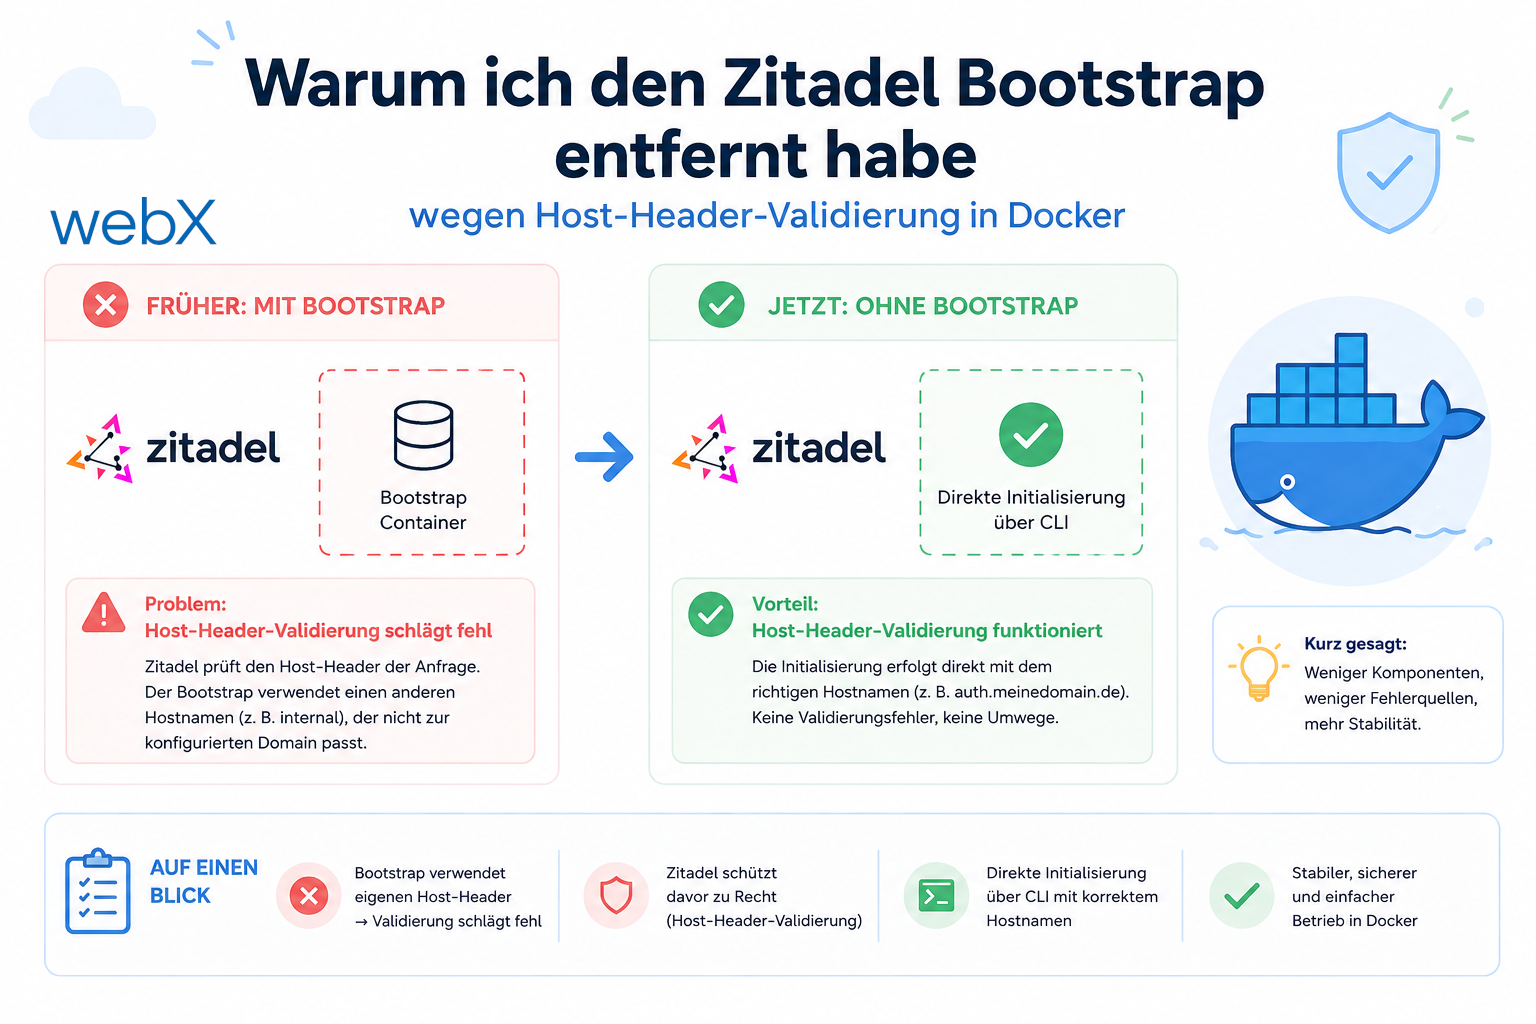
The bootstrap container exited with code 22. The cause was not an incorrect API URL, but Zitadel Host header validation inside the Docker network.
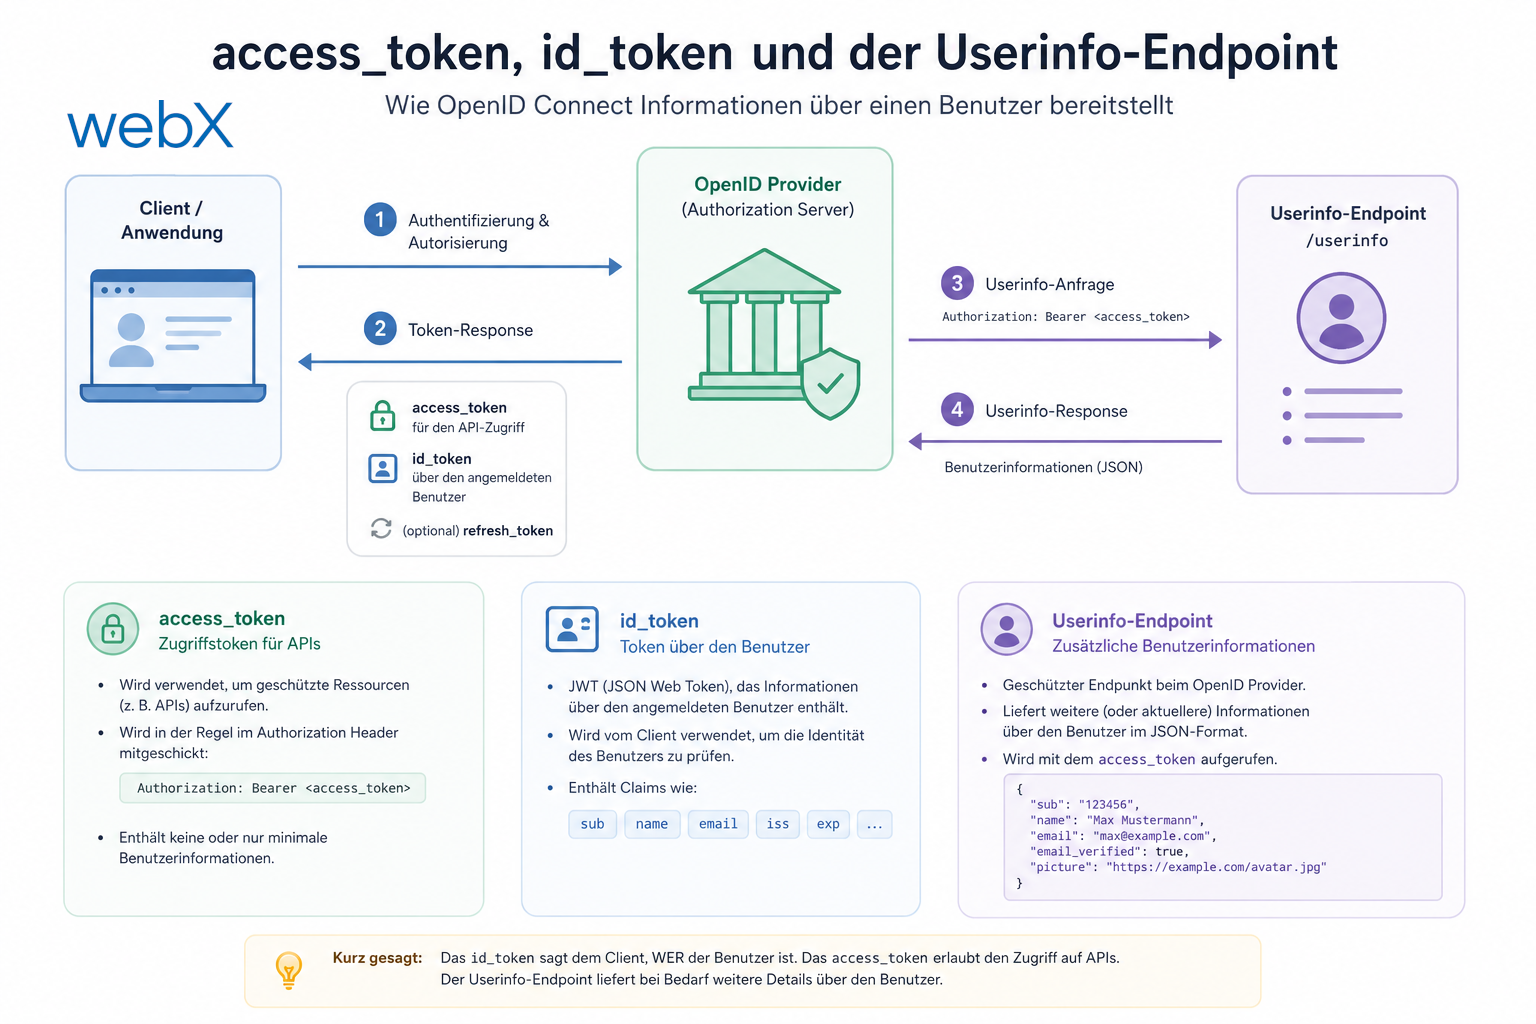
OAuth 2.0 and OIDC return two tokens at login, and almost every implementation reads the email address from the wrong one. Why access_token and id_token serve fundamentally different purposes, and why the Userinfo endpoint is the more reliable source for user profile data.
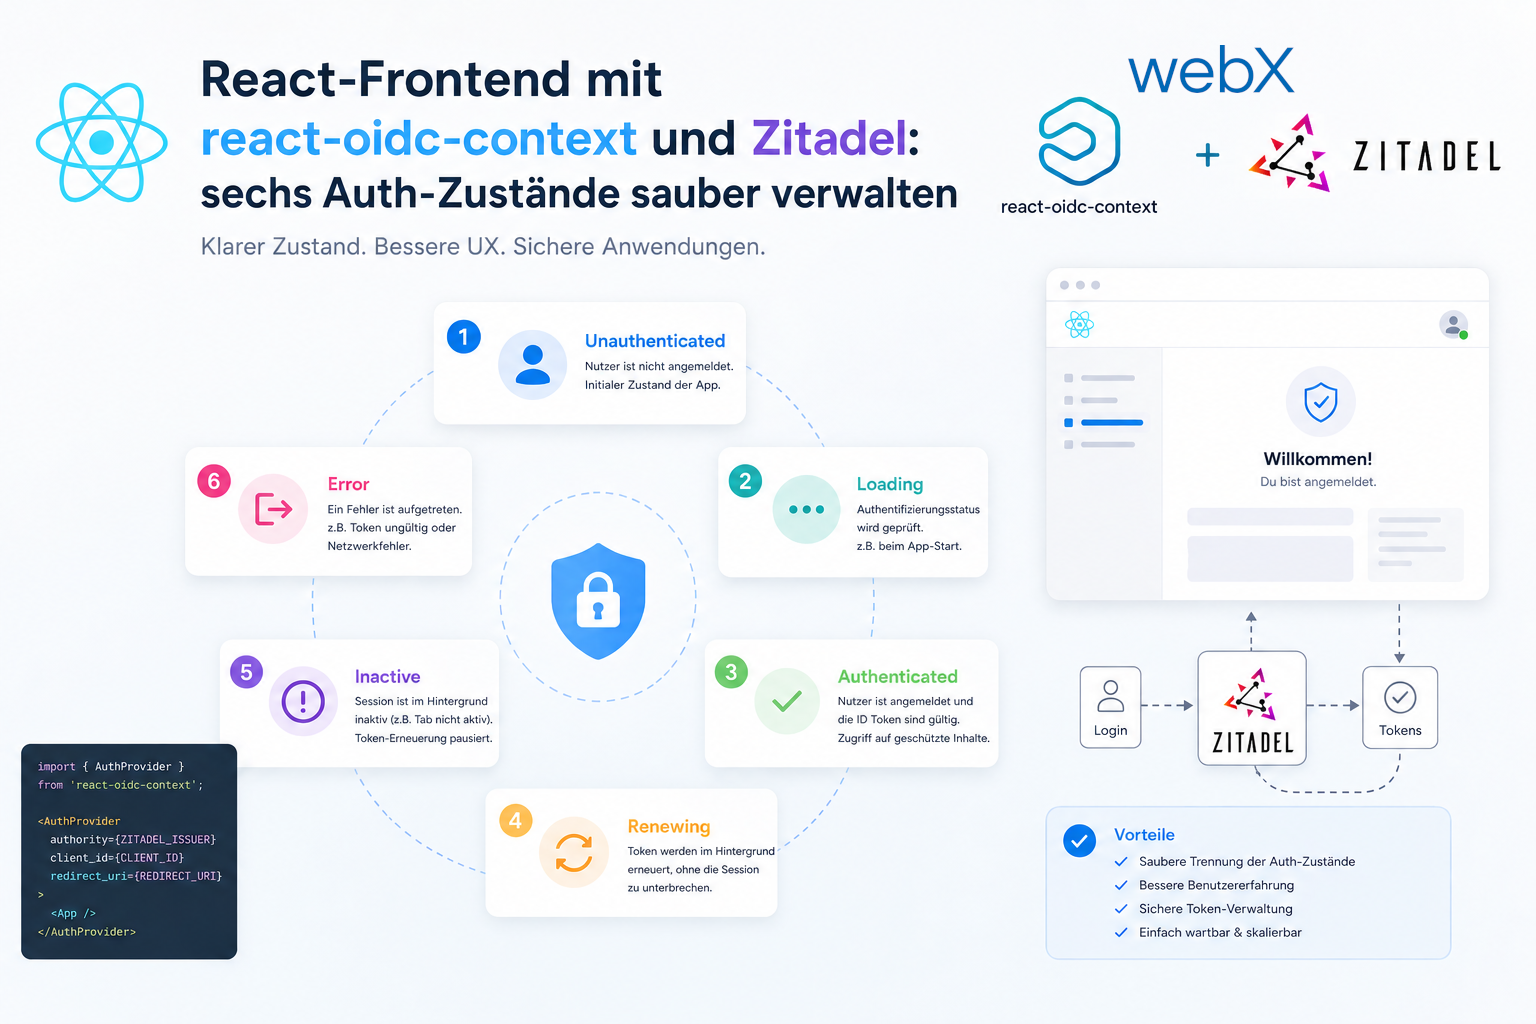
react-oidc-context handles the browser PKCE flow. The real challenge is not the login button, but correctly handling all six authentication states in App.tsx and backend JWT middleware using Zitadel’s JWKS endpoint.
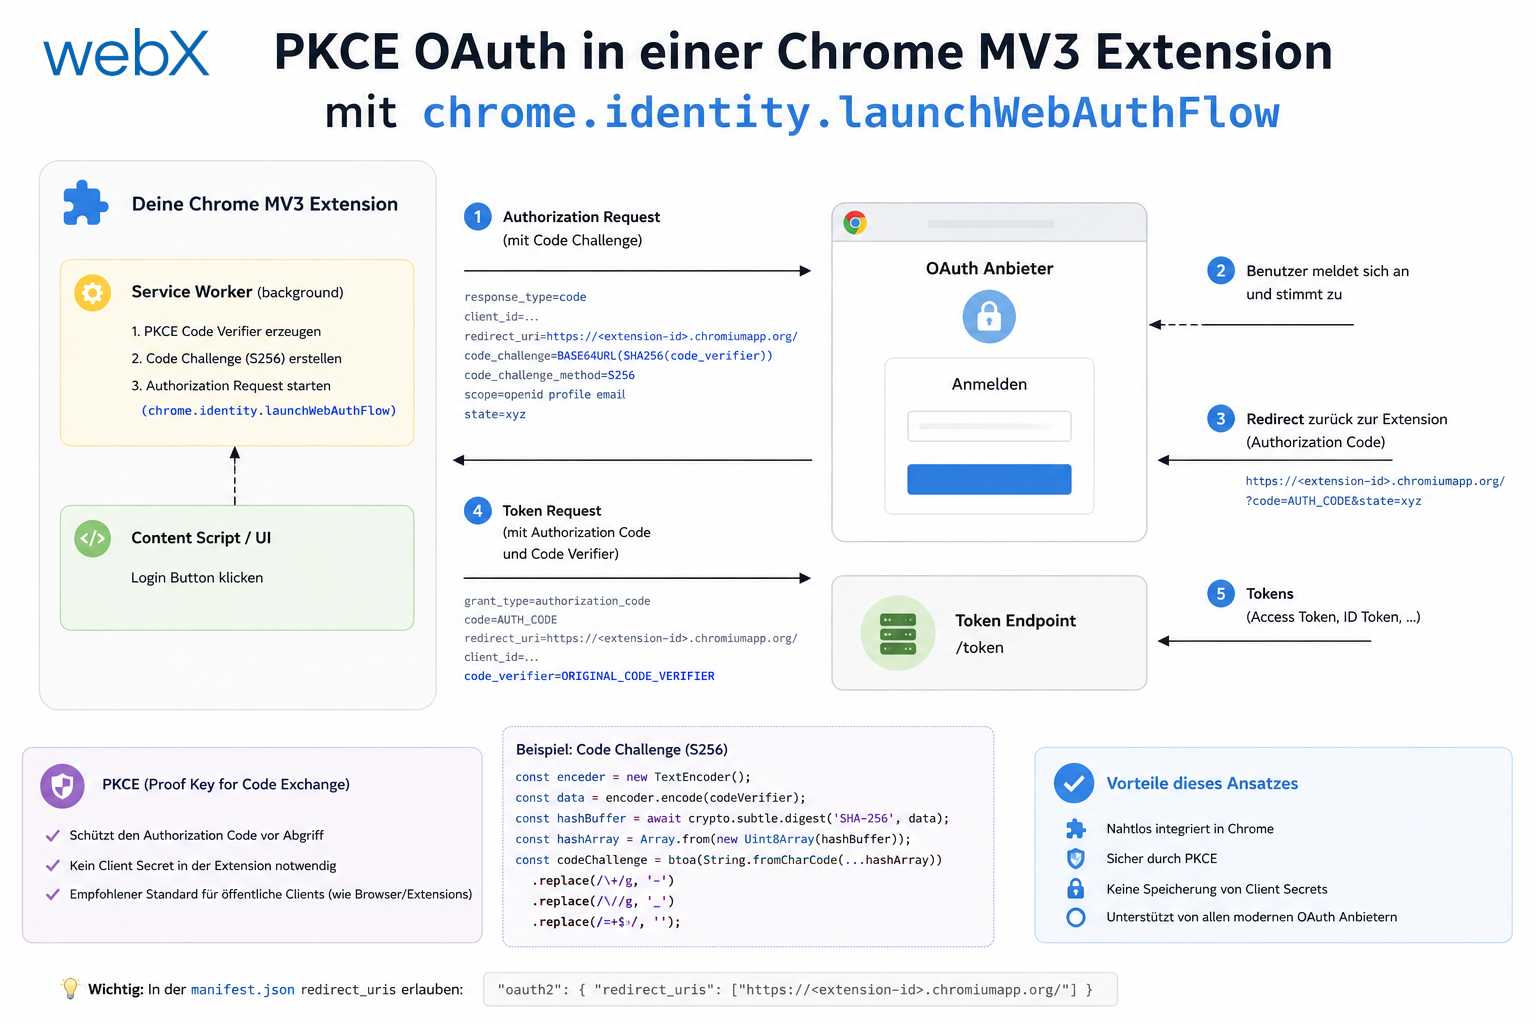
chrome.identity.launchWebAuthFlow is the right entry point for PKCE OAuth in Chrome Extensions. How token storage in chrome.storage.sync, automatic renewal and the extension-specific redirect URI work together.
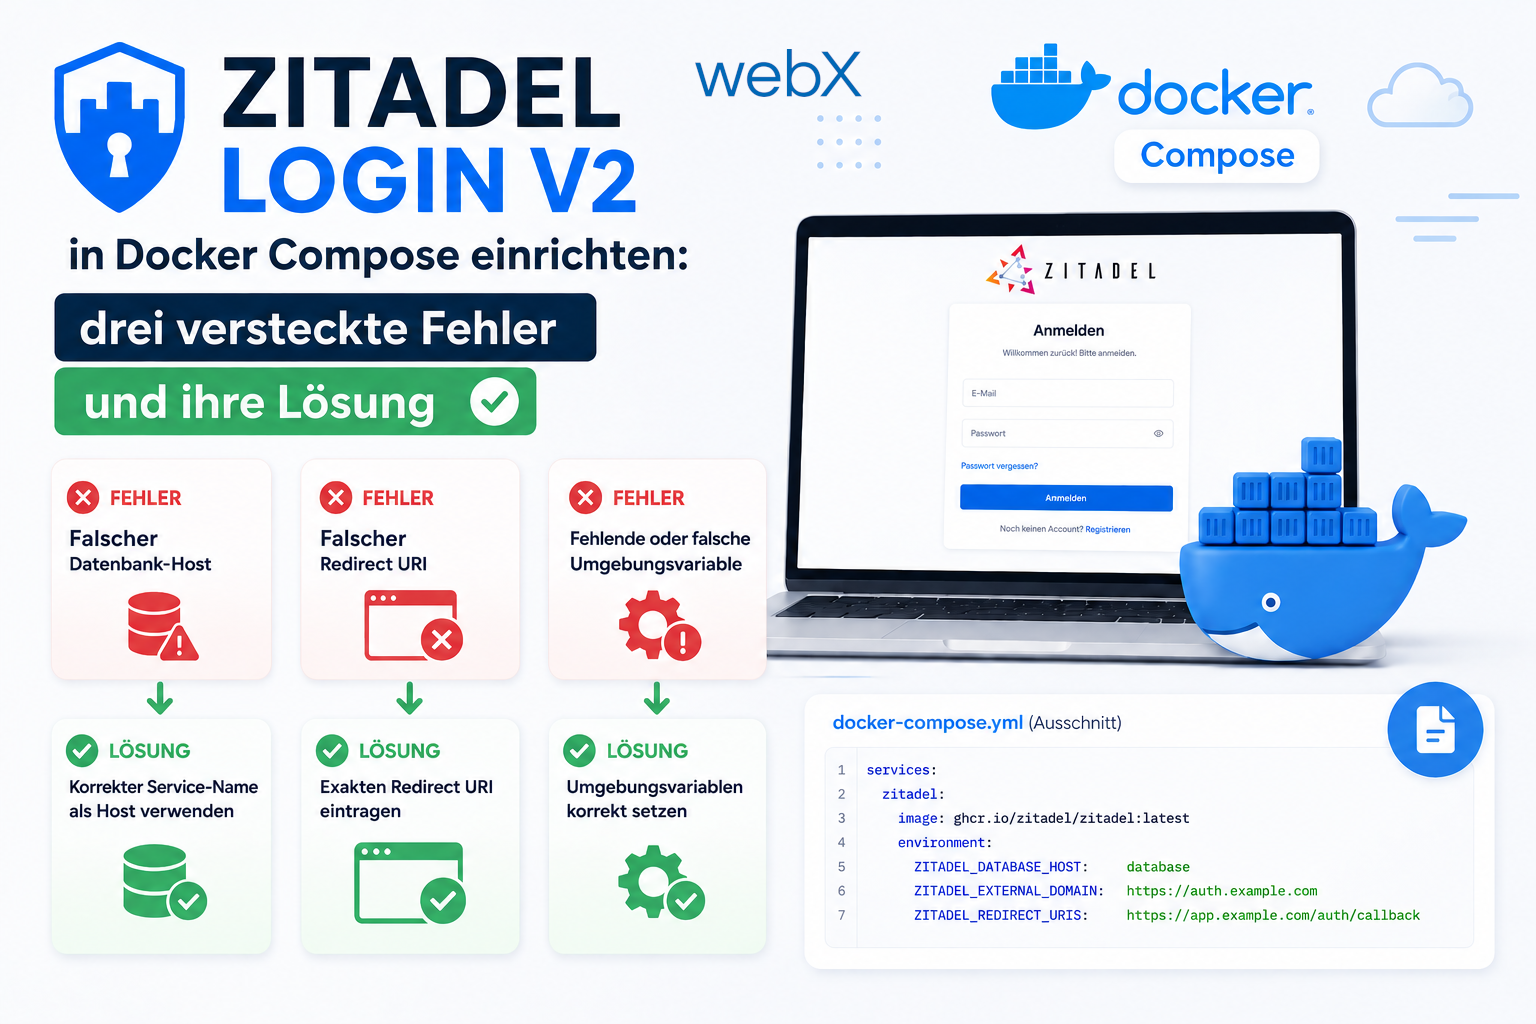
Zitadel v4 includes its own Next.js login UI. Setting it up in Docker Compose encounters three non-obvious problems: the Postgres 18 volume layout, missing PAT file permissions and incorrect BaseURI configuration.
Describe your workflow. Together, we will identify the right next step.
Discuss your workflow